For problem A and B, if there exists a computable function f that for all instance x∈A, A(x)=B(f(x)), we say that A could reduce to B.
Reduction (or simulation) is a powerful idea in computer science. Especially in cryptography, we use the idea of reduction to prove security of some cryptographic primitives.
We will illustrate the idea of reduction with a concrete example.
Example: Pseudo One-time Pad
Pseudo OTP:
Pseudo OTP solves OTP's drawback that secret key k needs to be as long as message m.
For m∈{0,1}n, we expand a short key k to the length n with PRG: r:=G(k). Pseudo OTP encrypts as c:=m⊕G(k).
Try to prove: Pseudo OTP Π is EAV-secure if G is a PRG.
We reduce "Pseudo OTP Π is EAV-secure" to "G is a PRG".
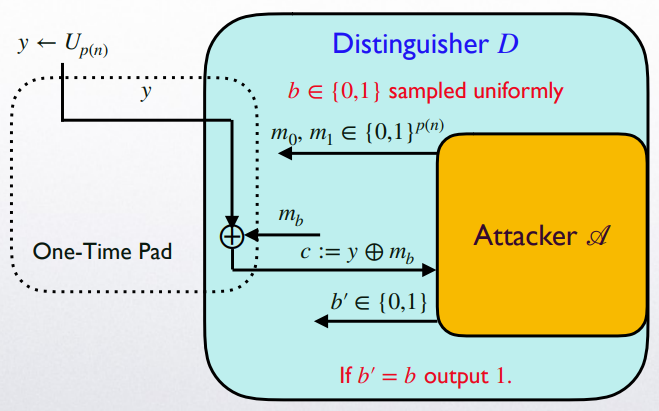
Construct a distinguisher D for Ggiven A attacking Π as its subroutine.
DrunsA(1n).
A outputs m0,m1.
D generates a random bit b∈{0,1} and obtain r from PRG challenger.
D sends mb⊕r back to A.
A finally outputs b′.
If b′=b, D outputs 1, otherwise 0.
reduction flowchart
Considering the following 2 cases:
r←Un is truly random
In this case, the view of A is distributed identically to that of a true OTP protocol Π which obeys perfect secrecy, therefore Prr←Un[D(r)=1]=Pr[b=b′]=Pr[PrivKA,Πeav(n)=1]=21.
r:=G(s) for some s (r is pseudorandom)
In this case, the view of A when run as a subroutine of D is that of the adversarial indistinguishability experiment of the Pseudo OTP Π, therefore Prs←Um[D(G(s))=1]=Pr[b=b′]=Pr[PrivKA,Πeav(n)=1].
Reduction process:
Since G is PRG: ∣Prr←Un[D(r)=1]−Prs←Um[D(G(s))=1]∣≤ε(n).
From the 2 equality above: ∣Pr[PrivKA,Πeav(n)=1]−Pr[PrivKA,Πeav(n)=1]∣≤ε(n).
Therefore Pr[PrivKA,Πeav(n)=1]≤ε(n)+21, which indicates that pseudo OTP is EAV-secure.
Reduction Logic
Reduction provides an abstraction.
Understand the abstraction is the key to understand reduction.
If we want to reduce the security of Π′ to the security of Π, we need to construct an adversary S for Πgiven the adversary A for Π′ as its subroutine, which is to say, S employs (runs) A as a black box abstraction function (Encapsulation).
The reduction involves 4 logic statements:
p:∃S that is able to attack Π with non-negligible advantage.
q:∃A that is able to attack Π′ with non-negligible advantage.
¬p:Π is secure, which means S that could successfully attack Π is NOT exist.
¬q:Π′ is secure, which means A that could successfully attack Π′ is NOT exist.
If S is constructed successfully, it will be able to attack Π with non-negligible advantage. Therefore we could conclude that if A could attack Π′ successfully, S (which takes A as its subroutine) could attack Π. The corresponding logic is q→p.
According to the contrapositive statement, we have ¬p→¬q, which implys that the security of Π guarantees the security of Π′. Therefore, the reduction is completed: we reduce the security of Π′ to the security of Π.
Contrapositive argument:
The contrapositive of the conditional statement "If p then q. " is "If not q then not p".
The logical equivalence could be expressed by p→q⟺¬q→¬p.
Eureka moment!
归约应该是整个密码学安全性证明中的核心思想之一。
第一次接触归约时 (即上文中提到的对伪一次性密码本安全性的证明) 真的思考了超级久才把整个逻辑捋清。但一旦想明白了就会觉得实在是巧妙:假设攻击方案 A 的敌手存在,我们直接将该敌手封装 (encapsulate) 起来作为攻击已知安全的方案 B 的敌手的子程序 (subroutine)。如果构建成功,根据逆否命题就能完成归约。
归约证明最难的地方应该在于 simulator S 的设计:其与子程序 A 的交互必须是黑盒式的,且无法让 A 察觉到与其互动的并不是 challenger C,而是某个 simulator S。